This is clearly something which bugs me about the Go ecosystem. It's way too coupled to a single Git provider. The approach to dependency management is neat otherwise but more care should be taken about avoiding this GitHub lock in.


Bad actors clearly want to compromise supply chains. Stay safe and keep your eyes open.
The article it refers to is interesting as well of course. Still it shines a crude light on the biases it has. We might have a way to fund libraries available via registries. That's a good thing... But it ignores a lot of what Free Software is about. We need solutions for more software than just a specific family of libraries.
There is truth here that our profession reinvents the wheel way to often. Some problem are solved, they don't need reinventing. Be careful on your dependencies though, this is where lies the tradeoff.
Interesting piece which shows very well the complexity of the hardware supply chain. The parts which matter the most are largely ignored by everyone.
Another attempt at easing the pain navigating the Rust crates ecosystem? It has its merits as well.
A nicely balanced view at Rust the language but also the ecosystem. It's not all pretty and real issues are looming.
Indeed, skipping the centralized package manager might be better in the long run.
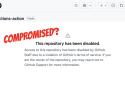
There's really something nasty at play. Those coding agents are clearly not insulated from the system enough and to easy to manipulate to exfiltrate sensitive information.
This is a good point. I feel unease at the current trend pushing toward cooldowns. The proposed rollout scheme is much better and fairer.
C++ too can have its own supply chain disasters with enough effort!
Can crates.io make things easier to secure? I do think so. But this post is right that we shouldn't forget the social aspect of the whole supply chain security conversation.
Indeed, the current supply chain model of Rust could be better. While we wait for improvements (with no sign of them coming), there are ways to try to avoid some of the common pitfalls.
Lots of interesting measures to reduce the risk of supply chain issues. Definitely to be considered on your projects.
We're not helped much by our tools here... Clearly provenance needs to be double checked.
New packaging ecosystems bring their new attack vectors. This is definitely a teething problem which will need to be addressed soon.
There are growing concerns regarding the Rust supply chain. It's still time to address them but it's became important to tackle this area.
Indeed, we might want to use dev containers more widely in the profession. If you're developing something for the desktop you're out of luck though.
Indeed, if you benefit from Free Software you'd better engage with it. Maintainers should stop bending backwards to please free loaders.
The idea is good, but it should be balanced with the necessity to react quickly when a new version is published with a fix for a vulnerability. It's not an easy balancing act when you keep both in mind.